
Low-Level Extraction the Apple TV 4K 2nd Generation
September 24th, 2026 by Vladimir KatalovCategory: «Elcomsoft News», «Mobile», «Tips & Tricks»
We’ve added bootloader-level low-level extraction support for the second-generation Apple TV 4K. While the older 4K model was compatible with the checkm8 exploit, the second-generation is based on a newer SoC that required a newer exploit, usbliter8. The exploit requires a custom adapter that uses a microcontroller board with our custom firmware.
Extracting the Apple TV 4K, 2nd Generation
What you need
- A Mac or a Linux computer with iOS Forensic Toolkit 10.11 (the Windows edition supports usbliter8 but is currently under testing)
- A microcontroller board with an RP2350 chip (Waveshare RP2350 USB-A is recommended)
- The usbliter8 firmware file for the board: https://github.com/Elcomsoft/usbliter8
- A Foxlink adapter (Apple TV 4K has no external USB port, but it has a hidden Lightning port below the RJ-45 connector; the Foxlink X892 GoldenEye adapter gives you access to this port)
- A DCSD adapter or a Colobus cable for DFU mode
Flash the board (one time only)
- Push and hold the button on the board
- Connect the board to the computer with the USB-C cable
- Release the button; the computer shows the board as a mass storage device
- Copy the usbliter8 firmware file to the board
- Wait some seconds; the board is now ready
Put the Apple TV into DFU mode: method A (DCSD adapter)
- Disconnect the Apple TV from the electrical power
- Connect the Foxlink adapter and the DCSD adapter to the Apple TV
- Connect the DCSD adapter to the computer
- Connect the Apple TV to the electrical power; the Apple TV goes to DFU mode automatically
Put the Apple TV into DFU mode: method B (Colobus cable)
- Connect the Foxlink adapter and the Colobus cable to the Apple TV
- Connect the Colobus cable to the computer (https://github.com/tihmstar/colobus_hardware)
- Connect the Apple TV to the electrical power
- Push the DFU button on the Colobus cable; Apple TV turns into DFU mode almost instantly
- Run
./EIFT_cmd infoto make sure that the Apple TV is in DFU mode
Apply the exploit
- Supply electrical power to the board through the USB-C connector
- Disconnect the Apple TV from the computer and connect it to the USB-A connector of the board
- Look at the indicator on the board: the indicator flashes two times, then it stays green (the exploit is applied)
- Disconnect the Apple TV from the board. and connect to the computer again
- Run
./EIFT_cmd info; the output shows that the Apple TV is in DFU mode and that usbliter8 is applied
You do not need the board again in this session.
The extraction commands
The commands are the same as the commands for checkm8 extractions of the first-generation Apple TV 4K. The articles at the end of this chapter give the full details.
| Command | Function |
|---|---|
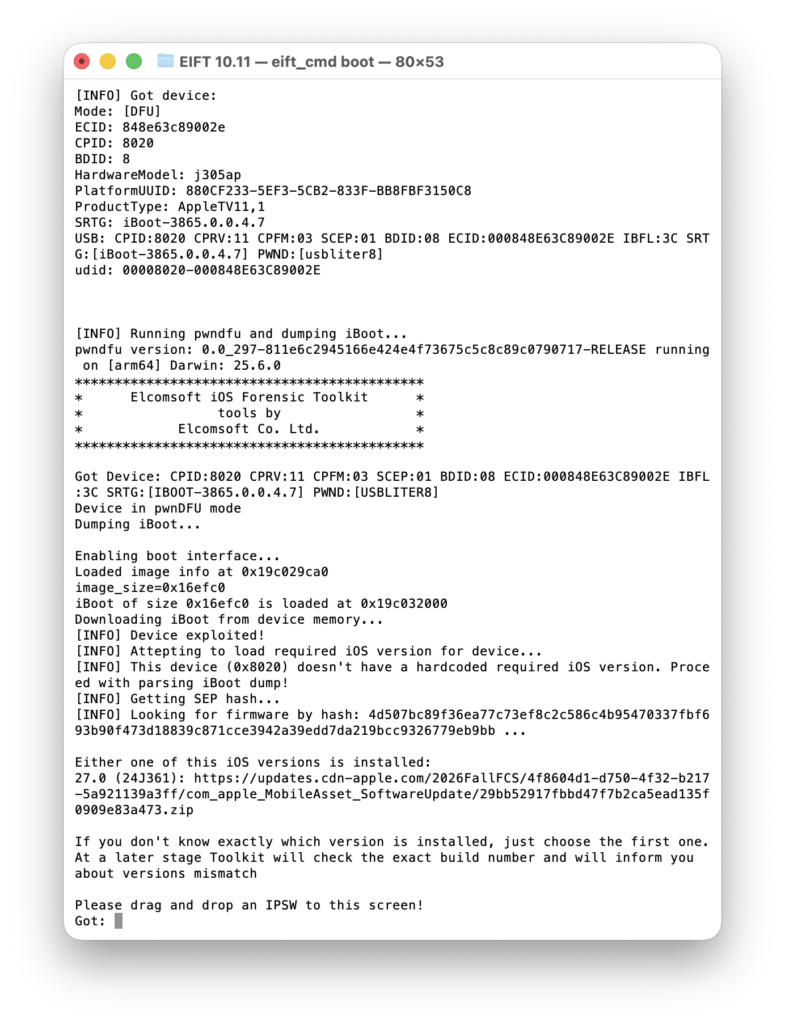
./EIFT_cmd boot |
Starts the ramdisk. The toolkit detects the version of tvOS and gives you one or more firmware links. Use the last link in the list. Full IPSW files for the Apple TV are rare; the toolkit also accepts OTA update images. |
./EIFT_cmd ramdisk unlockdata |
Unlocks the data partition and mounts it read-only. The toolkit does not ask for a passcode. If that doesn’t work, then use loadnfcd followed by unlockdata -s |
./EIFT_cmd ramdisk keychain -o {filename} |
Extracts and decrypts the keychain. |
./EIFT_cmd ramdisk tar -o {filename} |
Makes the image of the file system. The toolkit calculates the checksum during the extraction. |
./EIFT_cmd ssh halt |
Turns the Apple TV off. |
More information
- iOS Forensic Toolkit 8: Apple TV 3, 4, and 4K checkm8 Extraction Cheat Sheet
- Breaking Barriers: First Full File System Extraction from Apple TV 4K Running tvOS 26
- How to Put Apple TV 3 (2012-2013), Apple TV 4/HD (2015) and Apple TV 4K (2017) into DFU
- Apple TV Forensics 03: Analysis
- Using and Troubleshooting the checkm8 Exploit
- DFU Mode Cheat Sheet
Conclusion
You’ll need adapters and the microcontroller board, and you only need to flash the board once. The difficult step is the hardware, because you need the correct adapters for the hidden Lightning port. When the board shows the constant green indicator, the remaining steps are the usual bootloader extraction steps.
REFERENCES:
Elcomsoft iOS Forensic Toolkit
Extract critical evidence from Apple iOS devices in real time. Gain access to phone secrets including passwords and encryption keys, and decrypt the file system image with or without the original passcode. Physical and logical acquisition options for all 64-bit devices running all versions of iOS.
Elcomsoft iOS Forensic Toolkit official web page & downloads »
- iOS Forensic Toolkit 10.11: bootloader extraction for Apple Watch Series 4 and 5, Apple TV 4K 2nd Gen21 September, 2026
- Elcomsoft Quick Triage 2.2 adds a timeline, a plugin system, and file system snapshots3 September, 2026
- Elcomsoft System Recovery 8.38: Built-In BitLocker TPM Exploit Library, Browser Artefact Extraction, and Imaging Checksums26 August, 2026
- EIFT Firewall: a new free tool for controlled agent sideloading3 August, 2026
- Elcomsoft Phone Breaker 11.04: more reliable downloads from iCloud Drive30 July, 2026