Elcomsoft Quick Triage 2.2: Timeline, file system snapshot, and a plugin engine
September 3rd, 2026 by Oleg Afonin
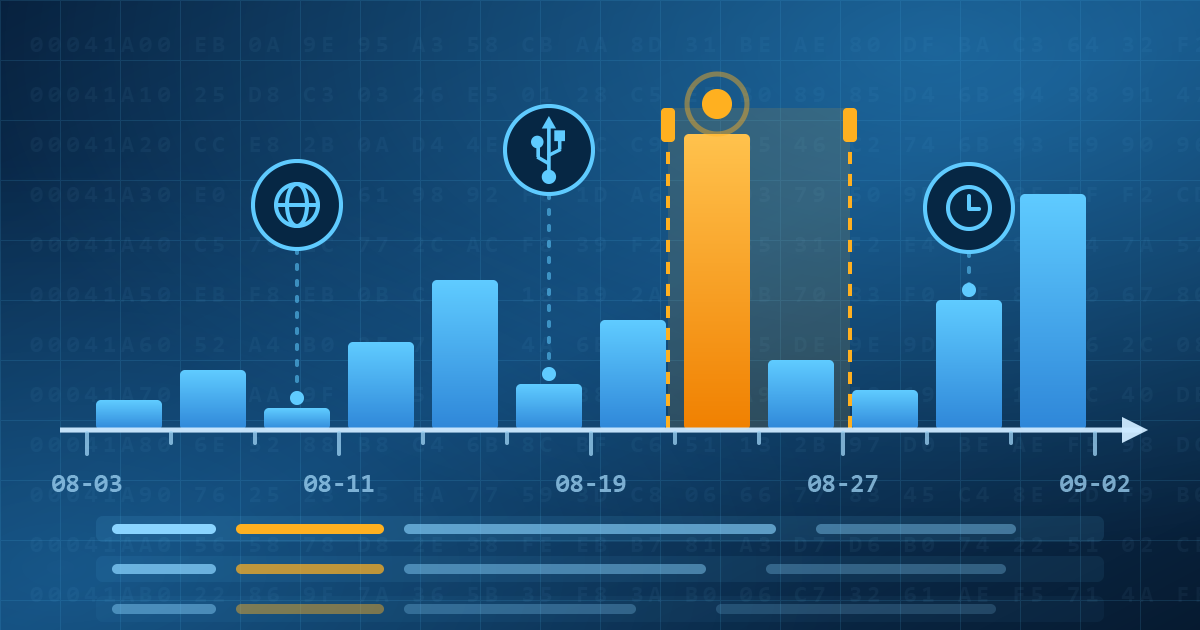
Elcomsoft Quick Triage 2.2 adds three things: a Timeline view that merges events from every timestamped artifact into one chronology, a file system snapshot that copies metadata without file contents, and a plugin architecture for artifact parsers. The release also brings MSA password attacks, OpenDocument parsing and recursive archive parsing in full-text search, and a list of fixes, but here we’ll mostly talk about the first three.
Password Managers: Security, Risks, and Forensic Implications
November 18th, 2025 by Oleg Afonin
Password managers have become a common part of everyday digital life, helping users handle hundreds of online accounts. They simplify authentication and reduce the need to remember complex credentials, yet the same centralization that makes them convenient also concentrates risk. Modern platforms from Apple, Google and Microsoft all ship with built-in password managers, and many users rely on third-party apps for the same purpose.
Breaking Barriers: First Full File System Extraction from Apple TV 4K Running tvOS 26
November 17th, 2025 by Vladimir Katalov
Big news is coming – and this time, it’s from the living room. Our team has successfully extracted a complete file system image from an Apple TV 4K running tvOS 26. This marks the first-ever low-level extraction of Apple’s 26th-generation operating systems, including iOS 26, iPadOS 26, and tvOS 26. No one – not even the major forensic players! – has been able to achieve this before.
Which Versions of iOS Are Supported, and Why “It Depends” Is The Best Answer
November 12th, 2025 by Oleg Afonin
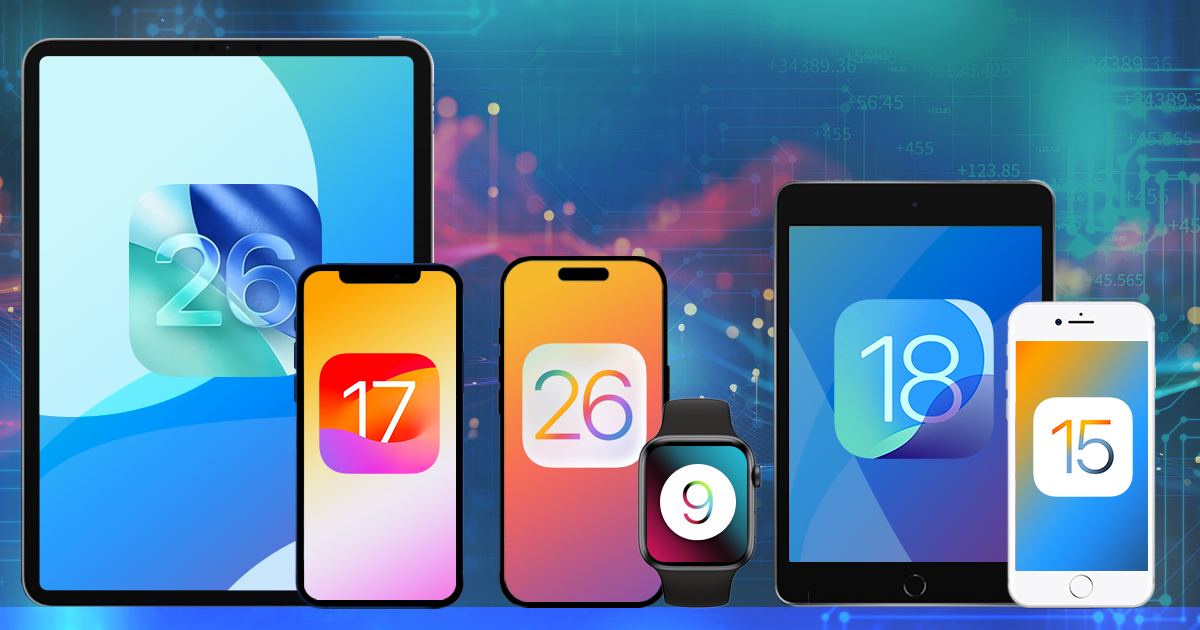
Our customers often ask us which exact iOS versions are supported by iOS Forensic Toolkit. There’s always a temptation to answer “all of them,” and while that answer is technically correct, there are a lot of caveats. The devil is in the details, and the real answer depends on what you mean by “support”.
Don’t Be a Louvre: How Weak Passwords and Unpatched Software Encourage Breaches
November 10th, 2025 by Oleg Afonin
During the recent investigation into the October 2025 Louvre Museum heist, it was revealed that parts of the museum’s video surveillance network were protected by the default password “Louvre.” Further reporting indicated that sections of the system operated on Windows Server 2003 and relied on outdated surveillance management software. These findings point to long-term neglect of basic cybersecurity practices – specifically, the continued use of obsolete systems and weak authentication measures.
Exploring iPadOS, tvOS and audioOS 17 and 18 Devices: File System and Keychain Extraction
November 6th, 2025 by Oleg Afonin
The latest update to iOS Forensic Toolkit brought bootloader-level extraction to a bunch of old iPads, Apple TVs, and even the first-gen HomePod running OS versions 17 and 18. This enabled full file system and keychain extraction on a those older Apple devices that can still run these versions of the OS.
All USB Cables Are Equal, But Some Are More Equal Than Others
October 17th, 2025 by Elcomsoft R&D
As we outlined in the previous article (Effective Disk Imaging: Ports, Hubs, and Power), it’s better to connect external USB-C devices (such as adapters and especially write-blockers) to a USB-C port that complies with at least the USB 3.2 Gen2 specs (10 Gbit/s). But what if your computer only has USB-A ports, or only a USB-A port is free? Obviously, you’ll need a USB-C to USB-A cable – but you’ll need to choose the right one very carefully, and that’s not the only thing that matters.
Effective Disk Imaging: Ports, Hubs, and Power
October 14th, 2025 by Elcomsoft R&D
Some time ago, we tested NVMe disk imaging performance (see When Speed Matters: Imaging Fast NVMe Drives), focusing mainly on software. This time, we turned our attention to hardware connections: which ports deliver the best results, and whether using a USB hub, active or passive, affects imaging speed and reliability.
Extracting Apple Unified Logs
October 13th, 2025 by Elcomsoft R&D
In our previous post, Extracting and Analyzing Apple sysdiagnose Logs, we explained the difference between sysdiagnose logs and Apple Unified Logs. Today we’ll show how the latest build of iOS Forensic Toolkit can pull Unified Logs directly from an iPhone or iPad during advanced logical extraction.
Cheat Sheet: Perfect Acquisition (32-bit)
October 13th, 2025 by Elcomsoft R&D
Perfect Acquisition is the most sophisticated method for extracting data from compatible iOS devices. This method is completely forensically sound; it doesn’t modify a single bit of the filesystem. When supported, this method should always be used over alternatives. This guide outlines the entire process, from acquiring the data dump to decrypting and mounting it for analysis. Note: this guide applies to iOS Forensic Toolkit 8.80 and newer, in which the process has been made easier to use.
Evidence Preservation: Why iPhone Data Can Expire
October 9th, 2025 by Elcomsoft R&D
When an iPhone is seized and later re-examined, forensic teams sometimes find that data present in an earlier extraction are missing from a subsequent backup or filesystem image. Why exactly does that happen, what kinds of data are affected, how long do they usually live, and what can you do to preserve volatile and semi-volatile artifacts? Let’s try to find out.


